NeuVector 获取触发 SQL Injection 告警的 SQL 语句
NeuVector 内置了 SQL Injection 检测规则。当 SQL 语句匹配相应规则时,会触发 SQL Injection 告警。
可以在 Notifications -> Security Events 中查看 SQL Injection 告警:
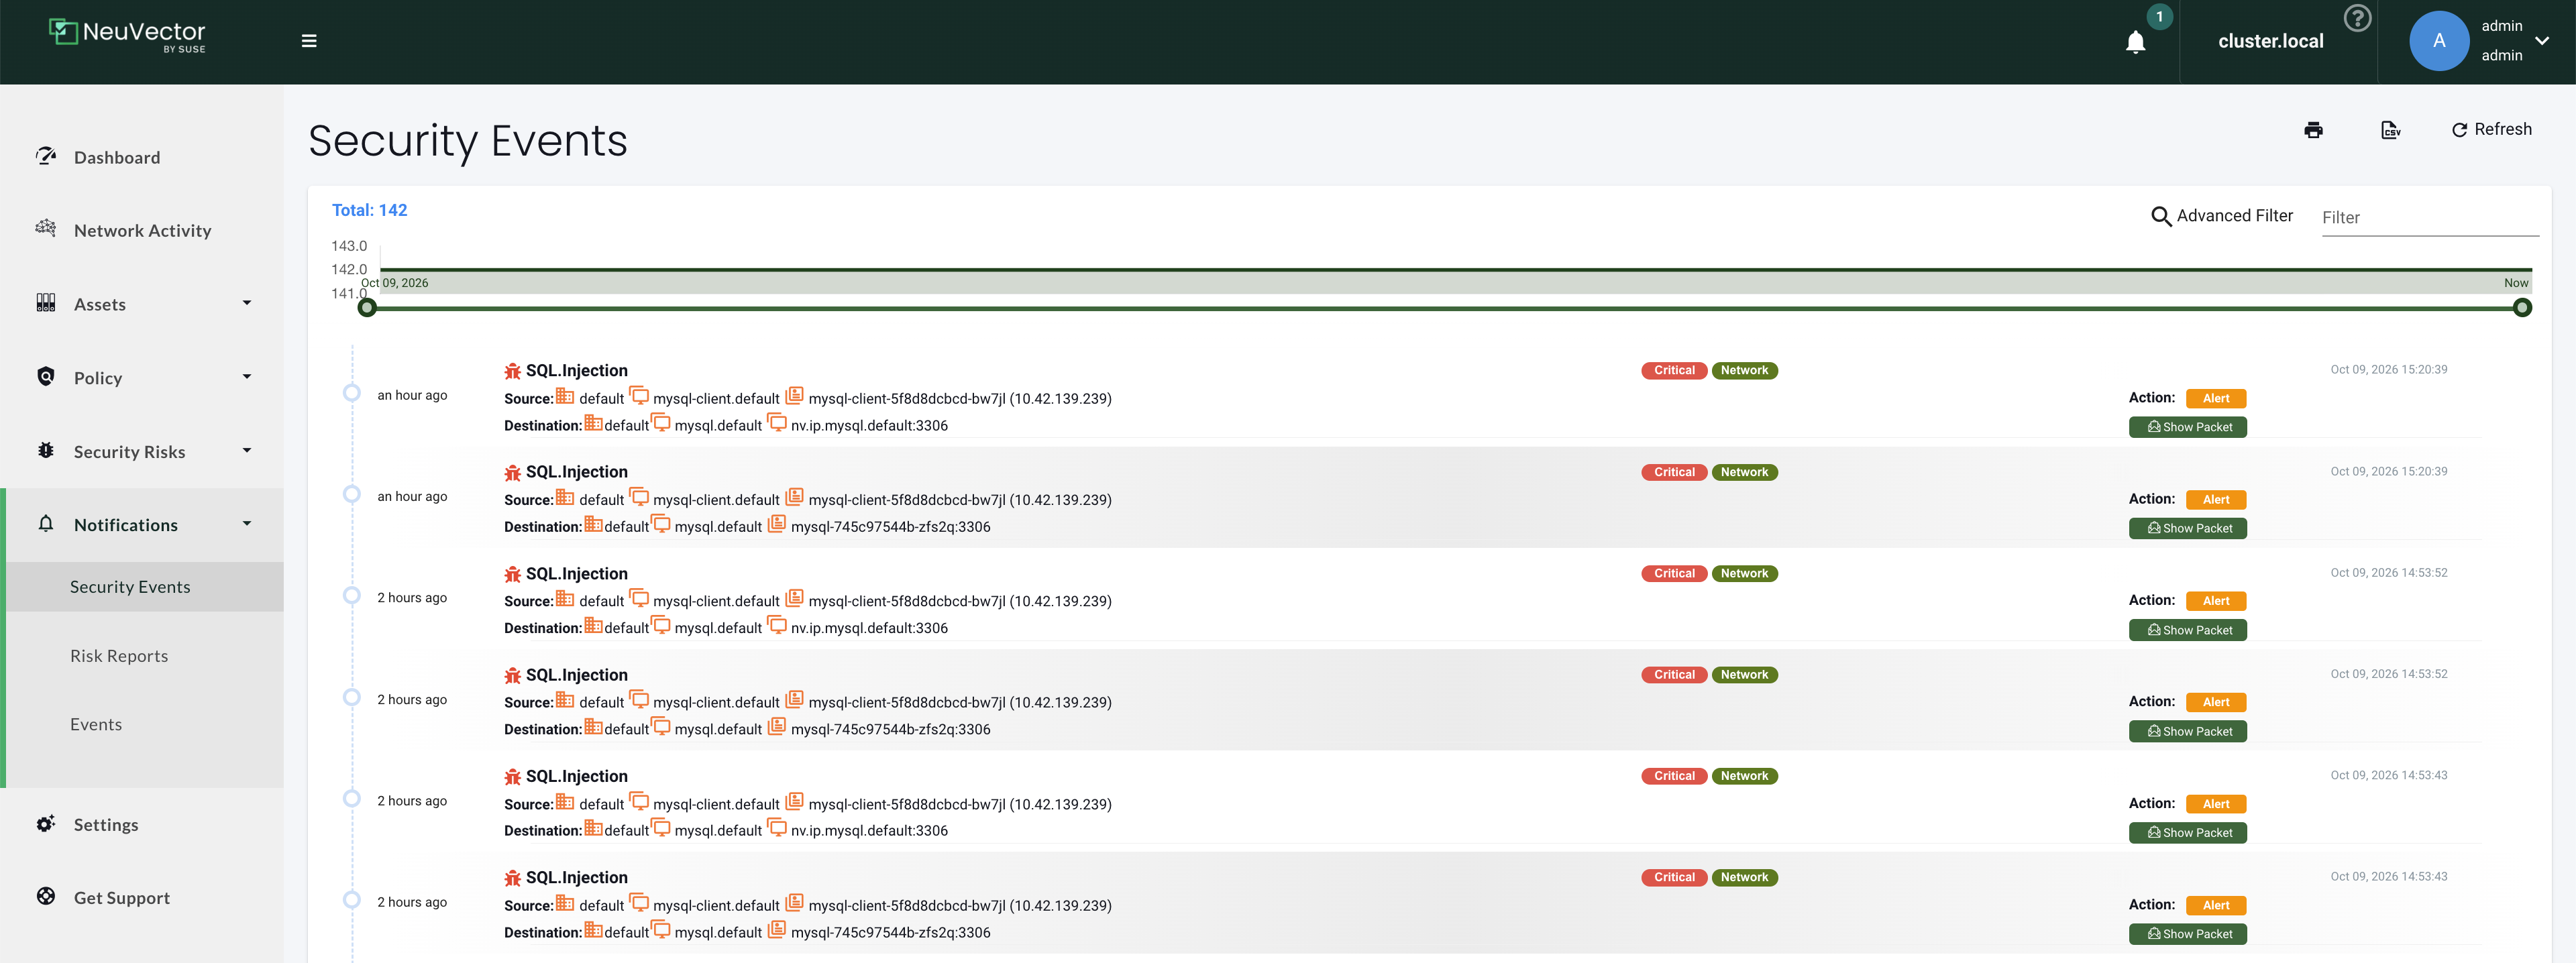
但是,告警详情中不会直接显示触发告警的完整 SQL 语句。如果需要获取对应的 SQL 语句,以判断是否存在误报,可以通过以下方式进行排查。
通过 PCAP 文件获取
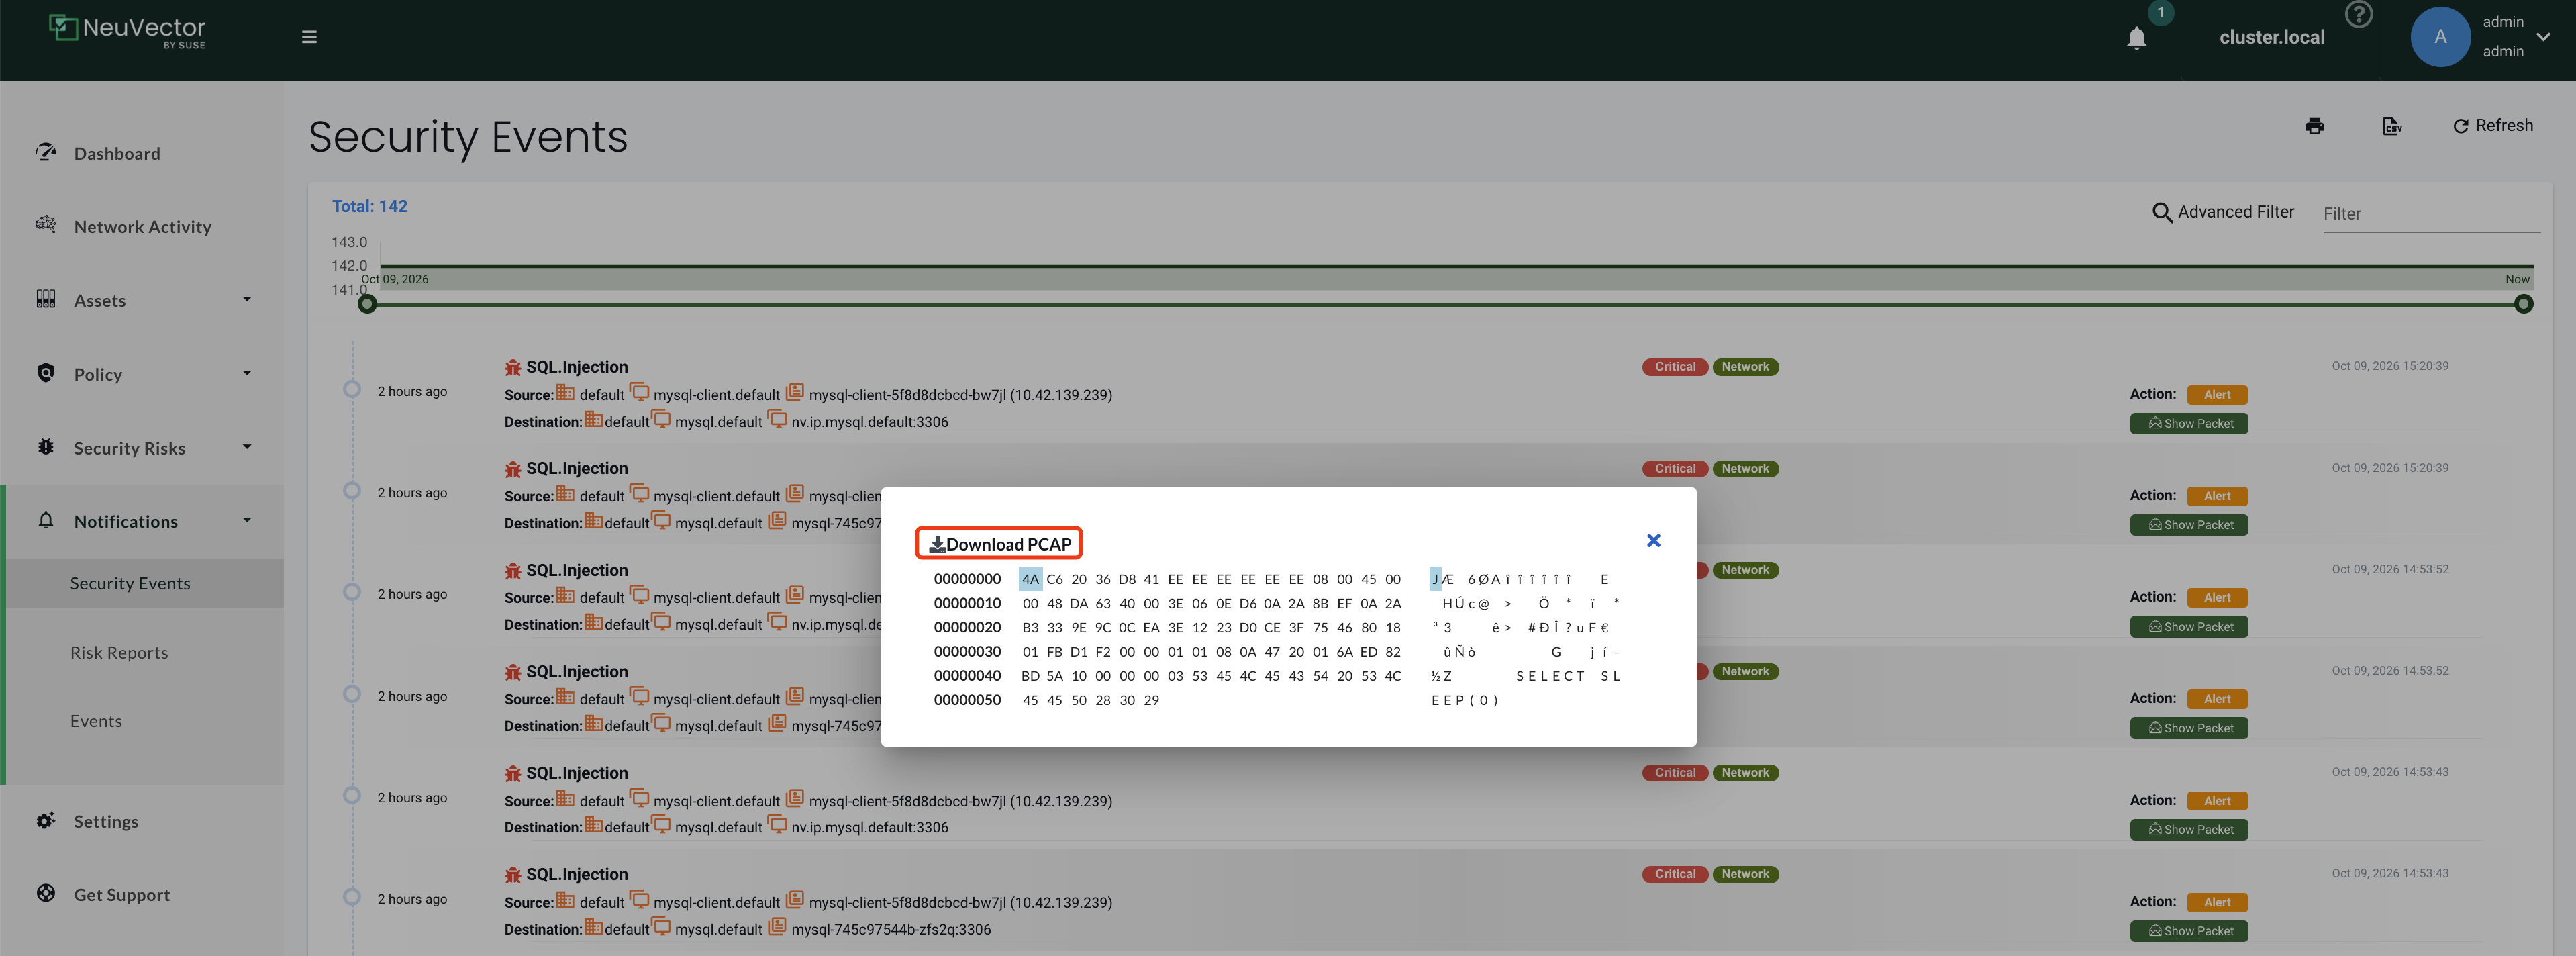
在告警详情中点击 Show Packet -> Download PCAP,下载对应的 PCAP 文件:
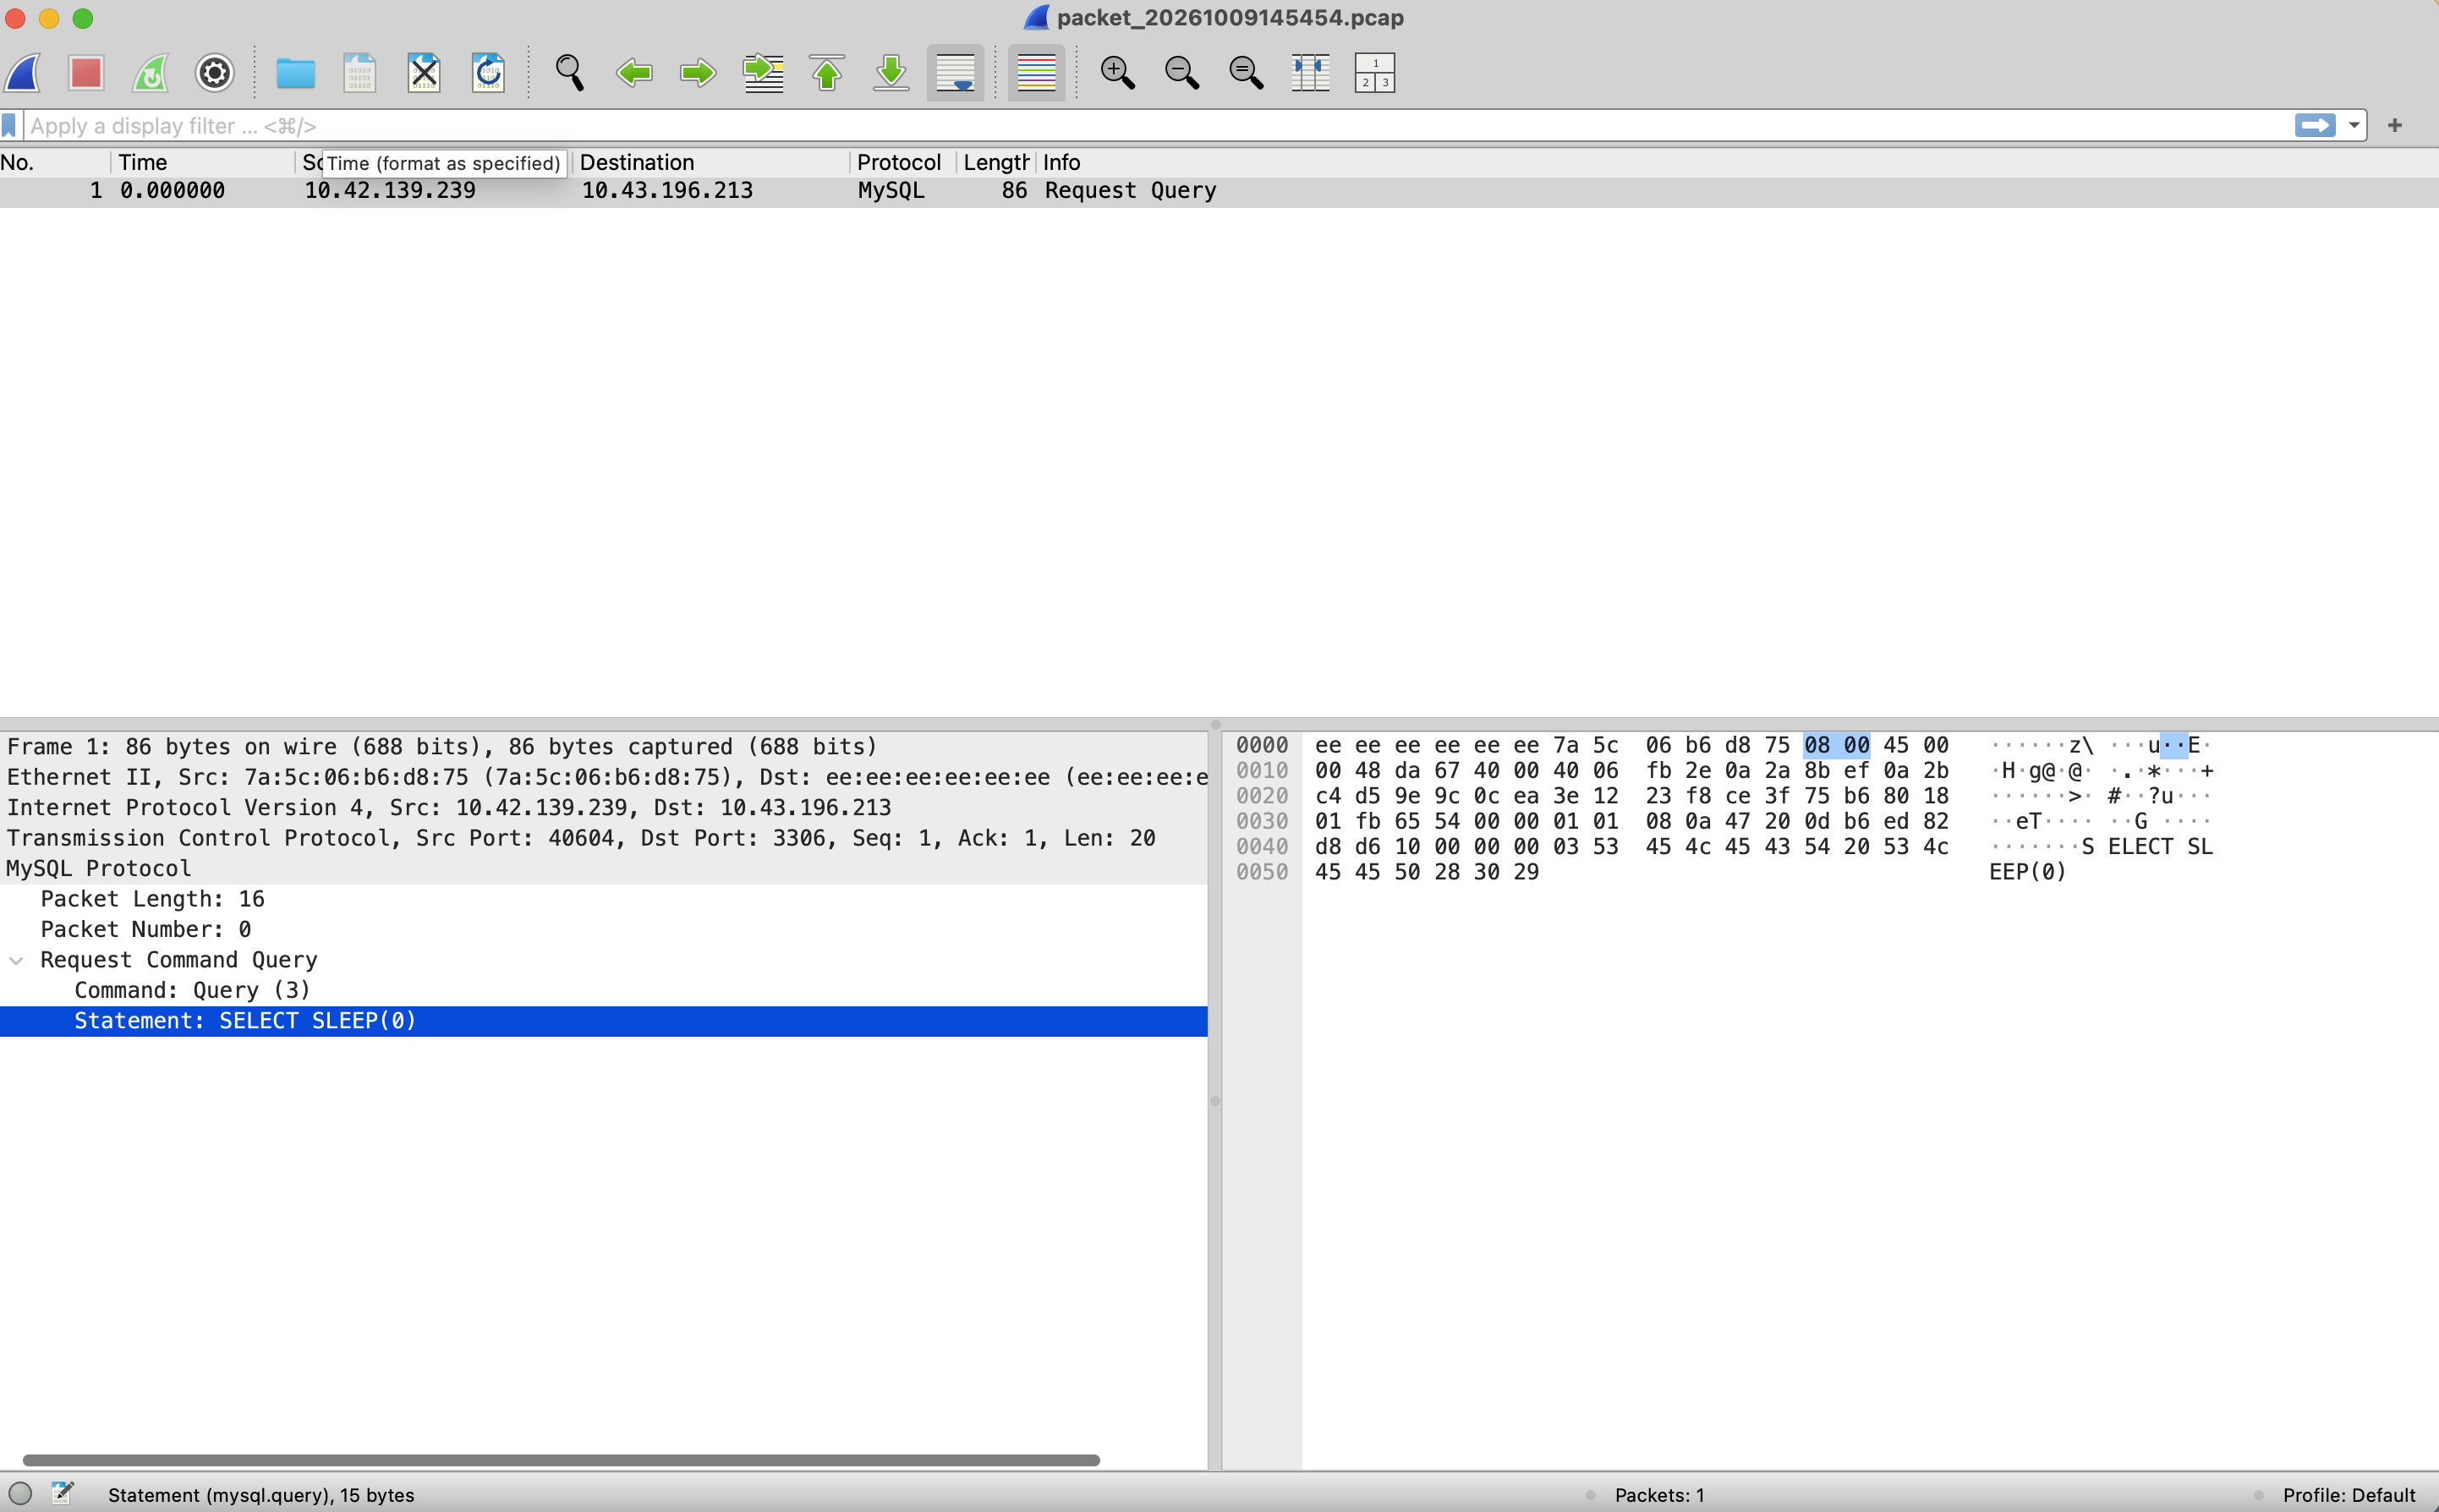
使用 Wireshark 等抓包分析工具打开 PCAP 文件,在 Statement 中查看对应的 SQL 语句:
通过 Controller REST API 获取
NeuVector Controller 提供以下 REST API,用于查询 Threat 事件及其详细信息:
1 | GET /v1/log/threat |
通过以下命令获取触发告警的数据包内容:
1 | # NeuVector Controller 连接信息 |
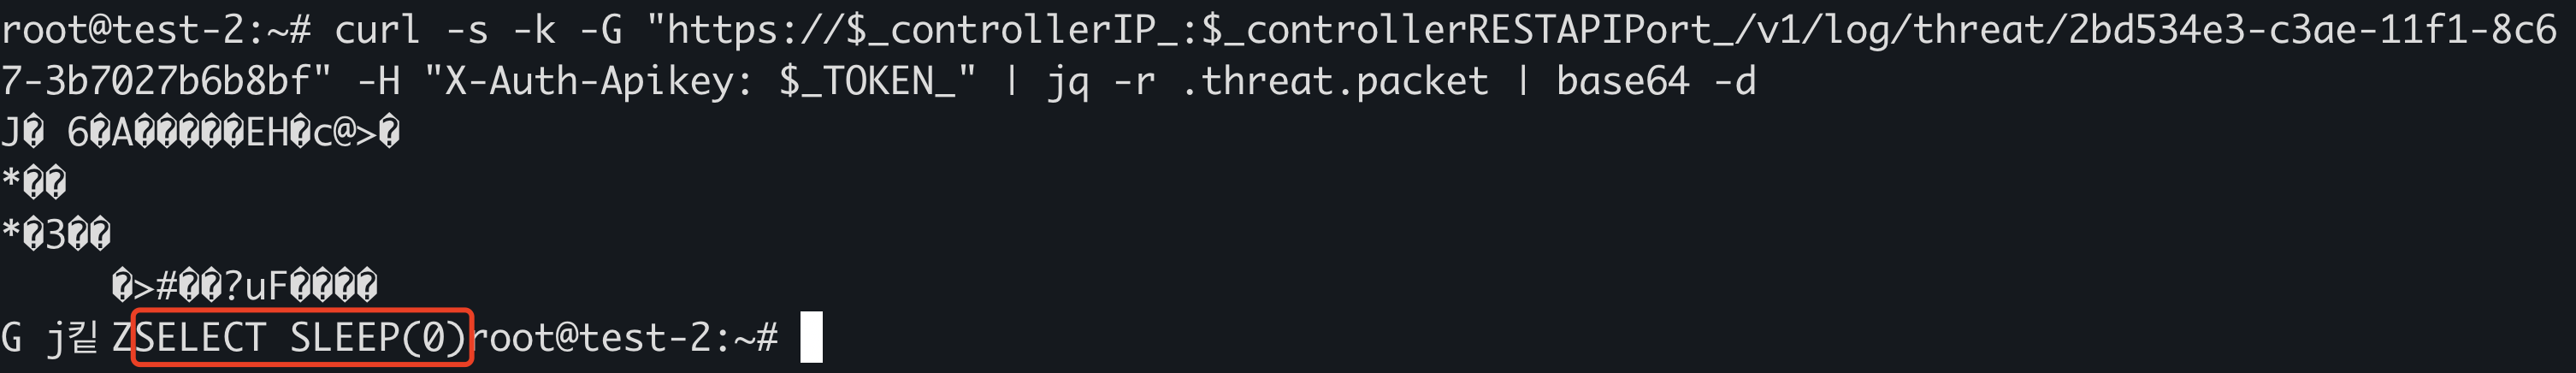
SQL Injection 告警最多保存触发告警的数据包中的 2048 字节,其中包含协议头。因此,对于较长的 SQL 语句或跨多个 TCP 数据包传输的 SQL 语句,获取到的内容可能不完整。
如果需要获取完整的 SQL 语句或网络会话,可以在 Network Activity 中右键点击客户端 Pod,启动 Packet Capture,然后重新执行测试并下载抓包文件进行分析。
NeuVector 获取触发 SQL Injection 告警的 SQL 语句
https://warnerchen.github.io/2026/10/10/NeuVector-获取触发-SQL-Injection-告警的-SQL-语句/